A Newbie’s Guide To The Compliance Galaxy
Sprinto’s guide for founders who sell to the US and beyond: when you need compliance, which framework to pick, and what the first audit takes, in order.
If I were a betting person, I’d say you’re probably reading this at midnight. Because your day job is, well, building the product, chasing your first customers, and getting your founding team to do big things.
Compliance? That’s probably not even what you had planned for your second shift. That is, until Bill from your dream top 10 list drops this on call: “you’ve got a SOC 2 report, right?”
Wait, what? Is this something you’re supposed to have already? What does it take to get one? And considering Bill’s willingness to spend, how quickly can you figure this out?
The good news? You’re right on schedule. Almost every founder who sells to the US and beyond hits this moment. Great timing for you and this article—consider this your guide to the compliance galaxy. Now for rule number one: Don’t panic. And if you do, don’t let Bill know.
While compliance can get jargon-heavy and technical, plenty of startups have done it before you. It isn’t an activity reserved for big companies with dedicated legal teams. It follows a fairly predictable checklist, and is a way to show customers, stakeholders, and investors that you can and will protect their data in accordance with applicable laws and security standards.
All it takes is good planning. And you’re in the right place.
Let’s start with when you actually need compliance.
When do you need compliance?
Here’s the short answer: For most startups, compliance only becomes necessary when you start selling. Think of it as something that helps you grow by assuring your customers that their data is safe. But it isn’t something you need to invest in immediately.
Some wise words from Reddit:
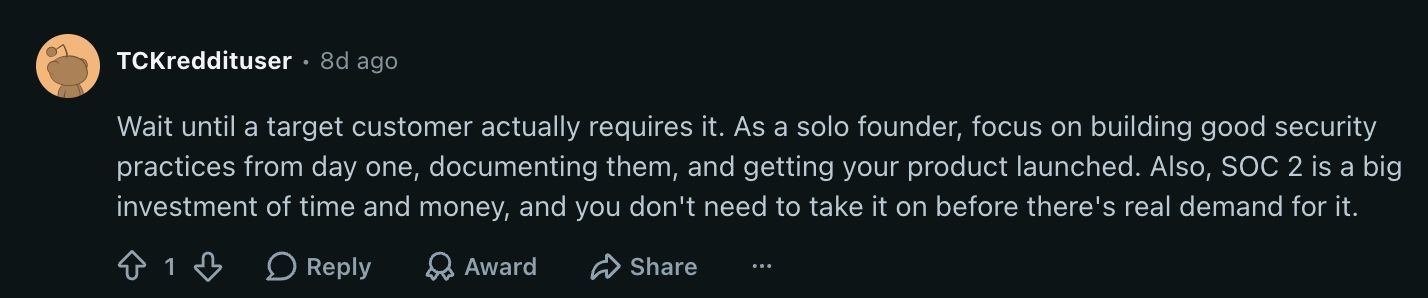
And here’s the long answer: In the early stages of starting up, compliance is at the bottom of your to-do list. Your product is changing on a weekly basis. Your first customers are likely small teams and early adopters who care more about what you’ve built than about your audit reports. And every hour you spend on paperwork is an hour you don’t spend on your product. So at this point, if no one is asking you for compliance, it’s perfectly fine to wait.
But this equation quickly changes as your product grows and as you sell upmarket. Your contracts get bigger, and deals start going through a procurement process rather than a founder handshake. Soon you start encountering compliance in the form of security reviews, questionnaires, and customer requests. And as you build towards mid-market, compliance becomes a standard, non-negotiable clause in customer contracts.
Too early for compliance if you don’t have paying customers or are still cracking product-market fit.
Too early for compliance if you’re only selling to consumers or smaller teams and no one on your customer list has mentioned security yet.
Consider compliance if your customers operate in a highly regulated industry or if you handle sensitive data such as payment card information, financial records, or personal data at scale.
Investors at Series A and beyond mention security and compliance in early conversations.
Accelerators in the US often ask about compliance early because their portfolio companies sell to enterprises.
Start compliance prep before you expect your first mid-market deal to close.
Compliance is non-negotiable at this stage. It shows up in contract discussions, security questionnaires, and sales conversations.
Not having it will likely stall deals.
Managing your first framework request
At its core, compliance starts with three questions:
- How do you protect data?
- How do you prove what you’ve stated?
- Can an independent auditor confirm it?
The tricky part is that every customer could ask these questions in different ways and expect different levels of detail in your answers. This is where a framework comes in.
A framework provides you with a set of guidelines and measures that spell out what good looks like. Complying with a framework involves implementing the appropriate set of controls, gathering evidence of compliance with its requirements, and finally, undergoing an audit. That’s where an independent expert, usually a licensed CPA firm or an accredited certification body, checks your controls and evidence against the framework’s requirements. This allows buyers to compare vendors against the same benchmarks.
A request for compliance may appear in many forms. Here are a few you may encounter:
Most of these requests come with a deadline in mind. You’ll often hear “we’d love to close this quarter.” Sure, this dials up the pressure and starts a silent countdown, but there’s no better reason to prioritize security and compliance. At an early stage, it isn’t an all-or-nothing scenario. Many customers will understand if you show them that you’re committed or present a letter stating that your audits are underway.
The payoff
If you’re feeling a little overwhelmed at this point, congratulations - you’re human!
Most founders find first-time compliance overwhelming. You’ve maybe just moved to a new country, you’re facing a new market, and now a buyer is asking you for something you’ve heard of in passing.
While compliance does sound like another problem to tackle, it pays off immensely when done right. In a recent conversation with Sprinto, Ryo Chiba, the Co-founder of Trails, explained that getting a SOC 2 report led to new inquiries.
But let’s dig a little deeper. Here’s what compliance gets you:
Faster deal closure
No more manual security questionnaires
Investor trust-building
Selling upmarket
Expanding to newer markets gets easier
Building a foundation for security
None of this really means you should rush into an audit, but it is a game-changer for winning bigger deals.
The building blocks of compliance
Compliance sometimes sounds like alphabet soup. While a lot of these terms can be daunting, it gets a lot easier once you learn how each of these terms relates.
In this section, we’ll cover three ideas you’ll keep running into: The key differences between regulations and frameworks, how certifications and attestations differ even though the terms are used interchangeably, and the relationship between controls, checks, and evidence.
Frameworks and regulations decide what you’re held accountable for, and certifications or attestations decide how that gets verified. But regardless of what you choose, the work underneath the hood remains consistent. Everything ties back to controls, checks, and evidence. They form the bedrock of compliance.
Regulations vs frameworks
SOC 2, HIPAA, GDPR, and ISO 27001 are often mentioned in the same breath. And this is where most founders get tangled up - not being able to tell which ones customers simply expect and which ones are mandated by law. Let’s clear this up.
Think of regulations as gravity: they apply whether you like it or not. These are laws that must be followed whether or not a customer asks for them. Breaching these or failing to adhere to them can result in hefty fines. Here are some examples of regulations you may come across in the US:
- HIPAA (applies to you if you handle health information, mandated by federal law)
- State privacy laws such as California’s CCPA (applies to you if you collect consumers’ personal information)
- Europe’s GDPR (applies to you if you’re based in the US but serve customers in Europe)
Frameworks, on the other hand, are more like your mission checklist your customers expect you to follow. They set out security guidelines that help organizations organize their security measures to effectively manage and mitigate cybersecurity risk. Frameworks and standards are completely voluntary—they aren’t laws, and regulators will not fine you for not adhering to them. But they may become a reason your mid-market and enterprise deals stall. Here are the frameworks you may come across:
- SOC 2 (A voluntary attestation created by the AICPA that serves as a default trust signal for software buyers in the US)
- ISO 27001 (A certification created by ISO for organizations handling sensitive information that applies if intending to sell to Europe, Asia, and the UK)
- NIST CSF (A voluntary standard developed by NIST for private organizations and widely expected of federal agencies and government contractors)
Certification vs Attestation
At the end of an audit, you’ll walk away with either a certificate or a report. At first, this might sound like a technicality, but it changes what you get, what your buyers read, and how often you must go through it to maintain compliance.
A certification is a formal stamp of approval. An accredited body assesses you against a fixed security standard and issues you a certificate indicating you adhere to it. The result here is black or white. You either pass the assessment, or you don’t. ISO 27001, for example, is a certification.
A certification is valid for three years but requires yearly surveillance audits to ensure you’re still adhering to the standard.
An attestation is an independent auditor’s written opinion and findings. Instead of a pass or fail, an attestation is a detailed report on what the auditor tested and what they found. SOC 2 is a well-known attestation.
An attestation, on the other hand, is typically valid for a year and must be renewed annually.
Controls, checks, and evidence
If regulations and frameworks set the rules, and certifications and attestations decide how you’re graded, then controls, checks, and evidence are where the groundwork happens. Every framework, no matter how different it looks on paper, runs on the same three components. Let’s break it down.
Controls are rules, policies, and safeguards you have in place to protect data. They cover everything from settings to everyday practices. For example, a control may specify that every company device must have disk encryption enabled and lock after 10 minutes of inactivity.
A check is a repeatable test that confirms whether a control is working as intended. A good check is one that is regular, repeatable, and assesses specific controls.
A device management tool, for example, runs a test to verify that every laptop in your company has disk encryption enabled and auto-lock switched on. This report is then reviewed to enable these settings on devices that do not have them enabled.
Evidence is the proof you hand an auditor. This includes screenshots, system exports, signed and acknowledged policies, and reviews. What the auditor is looking for is a timestamped piece of evidence extracted from the period you’re being audited.
A report detailing the status of disk encryption and auto-lock activation, along with any tickets listing the dates and fixes for flagged devices, would serve as strong evidence. And together, they prove that the control you have in place is functioning as intended.
This brings us to the term audit readiness. You’re audit-ready when your controls are in place, your checks show they're working as intended, and your evidence is collected, dated, and easy to find. And if an auditor decides to turn up tomorrow, you’re able to give them what they need without scrambling to fix gaps or dig out screenshots.
The Exam Analogy
Think of compliance as an exam you’re preparing for. Tap each part of the exam to see what it means in compliance terms.
The framework or regulation is your syllabus. It tells you what you’ll be tested on, but not how you study.
A certification or attestation is what your final grade will look like. A certification gives you a simple pass-or-fail. An attestation gives you a detailed report card.
Controls equate to the study plan you have in place. They’re the commitments you make to cover the syllabus. So a commitment like “practicing a test paper every Sunday” equates to “every laptop is encrypted and auto-locks after 10 minutes of inactivity” in compliance terms.
Checks are your mock exams. They don’t count towards your final result but tell you whether your study plan is actually working. Score badly, and you can go back and fix it before the real thing.
Evidence is the work you show for it—dated exam papers, mock test results, and notes. So if anyone asks you if you’re prepared, you don’t just say “trust me”; you actually show them.
An examiner (the auditor) tests you against the syllabus and looks for proof. And audit-readiness is knowing you’re sufficiently prepared. You’ve covered the syllabus, you’ve passed your mock exams, and you have proof to back it up.
Your Compliance Starter Kit
Here is a list of measures most startups put in place first, regardless of which framework they’re going after. Use it as a simple starting point. This is not an exhaustive list—your auditor may expect more, depending on your industry, product, team size, and infrastructure.
Your ticks stay in this browser only. They’re there to help you see where you stand today.
Frameworks you’ll most likely encounter
If you’re a tech company selling in the US, SOC 2 is almost certainly the first framework you’ll encounter. There’s a reason we’ve mentioned it so many times—SOC 2 is the default trust signal customers expect to see when they ask whether you’re secure. So let’s start there.
The essentials of SOC 2
What it is: SOC 2 is a framework created by the American Institute of Certified Public Accountants (AICPA), the US accounting body.
The framework is interpretive rather than prescriptive, which means it lists what you need to achieve, not what controls you implement. So you can design controls that you think best fit your business. A Certified Public Accountant (CPA) or a CPA firm then reviews these measures and compiles a report of their opinion and findings.
Who it applies to: SOC 2 is an attestation and applies to service organizations—any company that stores, processes, or handles customer data as a part of what it sells. This could include:
- SaaS and cloud service providers
- Data, analytics, or AI platforms
- Hosting, IT, and infrastructure service providers
- Financial technology, Healthcare, and HR service providers that sell to other companies
- Vendor products that plug into customer systems and data
What it covers: SOC 2 evaluates an organization’s controls based on five operational areas, known as ‘Trust Services Criteria’. These are:
Of these, Security is mandatory, while the others are included based on the nature of services offered.
Types of reports: There are two types of SOC 2 reports—Type 1 and Type 2.
A SOC 2 Type 1 report covers control design at a point in time.
A SOC 2 Type 2 report evaluates if your controls worked as intended over a period of time, typically 3 to 12 months.
Other frameworks and regulations you’ll likely encounter
Think of SOC 2 as your home planet. Everything else in the galaxy is a short trip from here.
It’s a common starting point for most early-stage companies, but it isn’t the only way in. It does, however, become your foundation while the ones listed below apply to you depending on which regions you sell to and what data you handle. You can pursue them alongside SOC 2 or even earlier if your market calls for it.
Unlike SOC 2, ISO 27001 is a certification from an accredited body. It sets out guidelines on building and maintaining what the International Organization for Standardization (ISO) calls an Information Security Management System (ISMS).
An ISMS is a structured set of policies, procedures, and technical controls designed to identify information security risks, evaluate them, and implement measures to minimize impact.
While US buyers prefer SOC 2, customers from Europe, the UK, the Middle East, and most of Asia prefer ISO 27001. Many founders who relocate to the US end up selling across two or more of these regions. So a combination of both frameworks is very common.
A significant number of ISO 27001 controls overlap with SOC 2. So if you’ve got the groundwork done for SOC 2, ISO 27001 becomes an extension of these efforts rather than a new project altogether.
The Health Insurance Portability and Accountability Act, HIPAA for short, is a US federal law and comes into effect if you handle Protected Health Information (PHI) for hospitals, clinics, insurers, or other healthcare organizations, including as their software provider. HIPAA is overseen by the US Department of Health and Human Services (HHS), which issues its rules, and enforced by the HHS Office for Civil Rights (OCR).
HIPAA has three key rules:
- Privacy rule (provides patients with certain rights, affording them better control over their PHI, and limiting how this data is used)
- Security rule (ensures the security of PHI that is collected, stored, processed, transmitted, and maintained by Covered Entities)
- Breach notification rule (requires Covered Entities and Business Associates to notify impacted parties and regulators about breaches within a stipulated timeframe)
It’s important to note that HIPAA does not have an official certification. Failing to comply with HIPAA carries hefty penalties, including fines, terminations, sanctions, and criminal charges.
HIPAA rules apply to two types of organizations—Covered Entities (healthcare providers, health plans, and healthcare clearinghouses), and Business Associates (organizations that handle PHI on behalf of Covered Entities or provide them with services).
If you’re a startup with healthcare organizations as customers, HIPAA applies to you. Customers will expect you to sign a BAA (Business Associate Agreement), a binding contract that guarantees you will keep their information safe.
SOC 2 covers a lot of the groundwork for HIPAA. HIPAA’s Security Rule specifically evaluates administrative, physical, and technical safeguards, and many of these overlap with SOC 2.
Having said that, HIPAA includes unique measures, such as the Breach Notification Rule, which sets deadlines for notifying affected parties and regulators.
The Payment Card Industry Data Security Standard, PCI DSS, for short, is a global security standard for the protection of cardholder data. First released in 2004, PCI DSS has been managed by the PCI Security Standards Council, founded by American Express, JCB, Discover, Visa, and Mastercard.
PCI DSS essentially covers security measures designed to ensure the safe and secure handling of cardholder data. The framework groups 12 core requirements under 6 vital goals:
- Build and maintain a secure network and systems
- Protect account data
- Maintain a vulnerability management program
- Implement strong access control measures
- Regularly monitor and test networks
- Maintain an Information Security Policy
Unlike SOC 2 and ISO 27001, non-compliance incurs fines ranging from $5k to $100k per month, depending on the duration. A breach can add to these costs, and companies can even lose the ability to accept card payments.
PCI DSS applies to any organization that collects, processes, transmits, and stores cardholder information. PCI DSS groups organizations into various levels based on the number of transactions processed per year.
PCI DSS is validated through a Self-Assessment Questionnaire or by a Qualified Security Assessor, depending on the organization's level.
Many controls from SOC 2 count towards both frameworks—MFA, unique accounts, encryption, written policies, and vendor reviews, to name a few. And while SOC 2 provides a strong foundation, PCI DSS requires its own scoping and validation.
ISO 42001 is the first international standard for AI management. Launched in 2023, it provides organizations with a structured approach to governing the development and use of AI. At its core, ISO 42001 provides guidelines for building and maintaining an AI Management System (AIMS).
Like ISO 27001, it’s a certification issued by an accredited body.
ISO 42001 applies to any organization that builds, uses, or sells AI systems. Startups fine-tuning their models or building features on a third-party model API can pursue the framework. While the certification is voluntary, it’s become a real differentiator for any company with AI at its center, especially for highly regulated industries like healthtech or finance.
ISO 42001 and SOC 2 overlap significantly in the foundational security layer. Risk assessment, policies, defined roles, and access controls are some ways they overlap. What SOC 2 doesn’t cover is the AI-specific layer, which includes measures such as human oversight, transparency, lifecycle controls, and impact assessments.
NIST, or the National Institute of Standards and Technology, is the institute that formalized its AI Risk Management Framework in 2023. It serves as a voluntary standard governing the management of risks arising from the development and use of AI.
The framework is built around four key functions:
- Govern: Setting up policies, roles, and culture for managing AI risk across the AI lifecycle
- Map: Understanding the context of AI—what it does, who it impacts, and what could go wrong
- Measure: Assessing and tracking risks through testing and monitoring
- Manage: Prioritizing risks, determining response, and keeping watch when things change
NIST AI RMF is designed for any organization that builds, deploys, or uses AI, regardless of size and industry. This includes startups building AI features on a third-party model API, not just large companies looking to build their own models.
The framework is voluntary, but matters most for AI-first companies looking to sell to US enterprises or working in regulated industries. Some state AI laws also designate it as a recognized framework.
Similar to ISO 42001, SOC 2 and NIST AI RMF have significant operational overlaps. The Govern step leans on the same written policies and defined roles under SOC 2. The Map and Measure steps build on SOC 2’s risk assessment and control monitoring, while the Manage step mirrors risk management and mitigation.
SOC 2 does not include the AI-specific layer addressing bias, fairness, explainability, and impact assessment.
NIST AI RMF is not a certification and does not involve an audit. That’s why many startups in the US align with the framework before moving on to ISO 42001 when customers request AI certification.
To sum up
See the whole table
You don’t need everything at once
Once you start reading about compliance, it sounds like an unending list of frameworks you need all at once. So here’s an important myth worth killing. Trying to do everything at once is how small teams burn out. Focus on one framework at a time, and add the next when customers ask.
The journey towards audit-readiness
You don’t need to have everything in place to start your journey, but it does involve homework. That means knowing where you stand, understanding what needs fixing, and collecting evidence as you go.
Start by taking an honest look at where you are today. Are you starting from scratch or do you already have policies and procedures in place? It’s important to be honest here, no matter how difficult it is. If you’re starting from scratch, you can use the Compliance Starter Kit to get started.
The flowchart below is what the audit-readiness journey typically looks like. It’s a good place to start for any framework you choose. But we’ll use SOC 2 as our example.
Step 1: Define the audit scope
Now that you’ve done your homework, it’s time to decide which systems and processes to include for the audit. Typically, for a first-time audit, this list should include your production environment and any systems that handle customer data. For SOC 2, you’ll need to decide which Trust Services Criteria to include, whether you’re aiming for a Type 1 or a Type 2 report, and if you’re choosing a Type 2 report, how long your observation period is going to be.
Next, integrate your tools. It helps to have a compliance automation platform that consolidates evidence across your environment.
Step 2: Find and fix gaps
Understand what the framework expects. Since SOC 2 is interpretive, there’s no fixed checklist. Instead, you map your existing controls to the TSCs and spot where they fall short. This gives you a clear picture of what you have and what you need done.
The next step is to identify the gaps—overlooked vendor reviews, unencrypted devices, and missing policies are the most common. If you’ve taken a look at the Compliance Starter Kit, then any policy or control you don’t have in place from there becomes your to-do list. Bucket these by priority and fix high-priority items first.
Step 3: Consolidate status
Track the status of your controls. Keep an eye on which controls are passing, how many are failing, and which ones need immediate attention. An audit dashboard becomes your mission control—your single source of truth, ensuring things don’t slip through the cracks.
Collect evidence as you go. For a Type 2 report, auditors want proof that your controls worked throughout the observation period, not just on the day they checked. Manual screenshots capture only a single moment and quickly go stale. This is why having a compliance platform that collects evidence automatically goes a long way.
Step 4: Conduct a readiness assessment
Consider the readiness assessment a dry run before the audit. It gives you a lot of context on just how audit-ready you are. It allows you to review every control against its evidence as an auditor would, either through an external advisor or through a compliance platform. Anything that falls short goes back into your fix list. This way, you avoid any surprises when your auditor arrives.
Step 5: Undergo an independent audit
Once you have everything in place, it’s time to undergo the audit. Start by picking the right audit partner—either a licensed CPA firm for SOC 2 or an accredited certification body for ISO standards. Look for partners with experience auditing startups and who can integrate with your compliance platform (if you have one). If you’re going for a Type 2 report, your controls need to run for an observation period before the auditor reviews their performance.
Don’t be afraid to compare quotes on the same scope.
What to expect during the audit
An audit typically starts with a kickoff meeting where the auditor reviews the scope and timeline with you upfront. Once agreed, you will receive a document that lists the data and evidence you need to provide. Over the next few weeks, the auditor will conduct walkthroughs and interviews to assess how controls work in the live environment.
Auditors will also pick samples (typically for a Type 2 report) across the observation period, such as code changes or new hires, and check each one against controls.
They will often request additional evidence and review it, typically taking 7 to 10 days per review cycle. They may even come back with follow-up questions and clarifications—this is completely normal.
An auditor is an independent reviewer and not a consultant. It’s important to see the relationship as such and understand what an auditor will and won’t do. They will not build or write policies for you. And while they tell you what’s broken, do not expect them to tell you exactly how to fix it.
What the results typically look like
At the end of an audit, you get a SOC 2 report with the auditor’s opinion on the front page. There are four possible opinions:
The smoothest landing—the best possible result. This indicates that your controls were presented fairly, are suitably designed, and operated effectively for the specified observation period.
This indicates that the audit was largely successful, except for one or more areas that matter.
This indicates that the auditor was not able to gather sufficient evidence and therefore was not able to form an opinion.
A rare scenario in which an auditor is of the opinion that your controls do not meet the required criteria. This happens when an organization undergoes an audit before it is ready.
Exceptions are specific instances in which an auditor found a control that didn’t work as intended, such as the one employee who promises to “complete security training right after this sprint.” They are very common, even for clean reports. What’s important here is that you acknowledge and address them.
Buyers will often look for a short management response, explaining what you did to resolve these exceptions.
When it comes to ISO, nonconformities are equivalent to exceptions. Nonconformities are classified as major (severe failures that critically impact the capabilities of an ISMS) and minor (minor lapses that do not critically impact the capability of an ISMS). Major nonconformities need to be resolved before you’re certified, whereas minor nonconformities require a corrective action plan.
The complete SOC 2 timeline
- Understand where you are
- Decide which systems fall within scope
- Integrate tools with a compliance platform
- Implement policies
- Identify gaps
- Bucket gaps, fix by priority
- Implement an audit dashboard
- Monitor control status
- Collect evidence as you go
- Conduct a readiness assessment
- Fix gaps
- Choose an audit partner
- Observation period
- Undergo an audit
A breakdown of costs
Alright. Let’s talk money. For most early-stage companies, the first SOC 2 report costs around $14k to $18k in year one if you pick a compliance automation platform or $19.5k to $28.5k if you go the manual route, for the Security criterion alone. This estimate includes tooling, testing, auditor fees, and an approximation to account for team bandwidth and resources (if done manually).
Treat these as ballpark figures, not an exact quote.
$2.5k for additional TSCsTSCs, observation period, scoped systems, audit firm chosen
*Cost of manpower is the value of the time your team spends on compliance work a platform would otherwise handle, like collecting evidence by hand, tracking controls in spreadsheets and chasing screenshots. It doesn’t appear on any invoice, but it adds up.
The totals above add up the rows in Sprinto’s table. The platform total leaves out the manpower row, and the manual total leaves out the platform row.
What to do next
An audit isn’t the finish line. Once your report lands, it’s tempting to file it away and get back to building your product. But your controls need to keep running because your next observation period begins as soon as the previous one ends.
The good news is that year two is far easier than the first one, as long as you keep the good habits going. Here’s how you close the loop:
Cleared for takeoff
If you’ve made it this far, give yourself a pat on the back. You’ve just sat through an entire chapter on compliance and lived to tell the tale.
A little while ago, SOC 2 was something you nodded along to in meetings while quietly googling it under the table. Now you know what it is, when you need it, and how to get started. And that’s more than many founders moving to the US can say.
Yes, it’s work—there are policies to write, evidence to chase down, and at least one moment you’ll find yourself documenting the fact that you documented something. But compliance is far more predictable than it looks. Do it properly, and it pays you back long after your auditor has gone home.
Compliance is huge, but you only need to explore the corner of the galaxy your customers live in. And now you have a map.